marketing
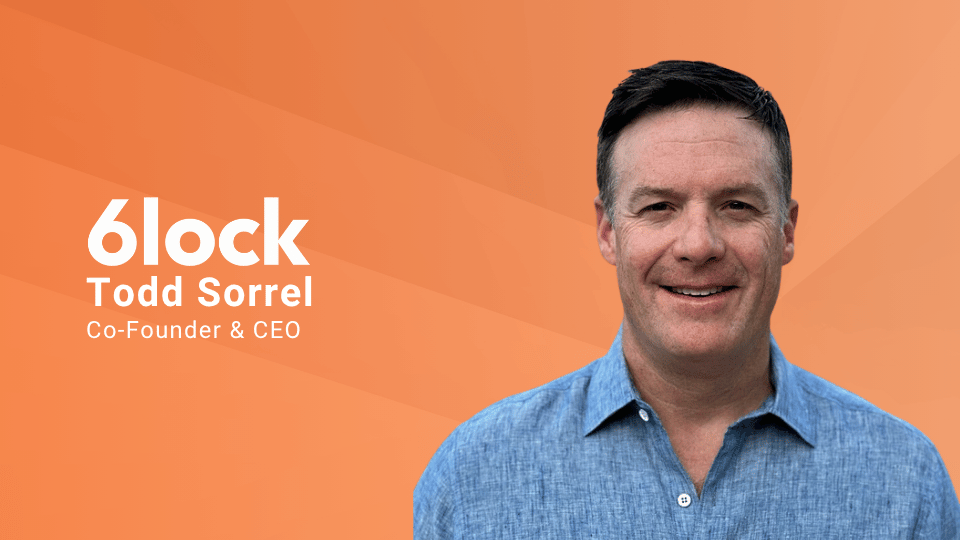
AI-Driven Fraud Is Reshaping Security in Private Markets, Says 6lock CEO
1. Private markets fraud isn't new, but the AI layer is. Was there a specific incident or pattern you encountered that convinced you this was the moment to act?
Two things caught my attention. The first was that wire fraud kept growing faster than the security tools and protocols built for private markets. The second came out of our discovery process. Every firm we interviewed executed fund flows in pretty much the same way, and AUM made no difference. It was spreadsheets, human review of PII, callbacks, bank portal uploads, bank templates, and emails back and forth. Sensitive data ended up sitting in multiple places, and every one of those places is an attack vector. Once AI made impersonation cheap, a process that looked identical at every firm became something an attacker could learn once and use everywhere.
2. Walk us through what an AI-driven fraud attempt looks like today. What does a convincing voice-cloning or deepfake attack look like in practice?
It rarely looks dramatic. The head of a company has a phone call with someone who reproduced his/her boss's voice, accent, and cadence. Nothing he heard gave him a reason to doubt it. He or she then wires hundreds of thousands of dollars. Attackers are building entire video calls of familiar colleagues. What makes these attacks convincing is preparation. Attackers study email threads, communication patterns, and travel schedules before they strike, so the request arrives with the timing, tone, and formatting of every legitimate one before it.
3. Business email compromise has been around for years, but you've said it's now moving faster than compliance frameworks can track. What's changed on the attacker side that's outpacing the defenses?
The grammatical red flags compliance teams trained employees to spot are gone. Compliance frameworks are built around known controls like callbacks, PDF instructions, and inbox approvals, and attackers now go after those. They can alter wire instructions that are in transit or clone the voice of someone who is on the other end of the callback. One of our clients got a call from an LP asking to confirm capital call instructions, which is routine in a manual process. The GP had never issued a capital call. The LP had received a spoofed email convincing enough that they were about to wire funds to a fraudster, and the GP only found out because the LP happened to pick up the phone. The LP’s problem quickly became the GP’s problem too.
4. Private market transactions often rely on relationships and trust built over years. How does that trust become a liability when someone can impersonate a known counterparty?
Familiarity is what social engineering is built to exploit. The more confident a team is that they'd recognize their fund administrator's voice, or their LP's writing style, the less likely they are to double-check. That’s what the attacker counts on.
Trust built over years is valuable, but private markets need to keep the relationship, and verify identity and instructions independently.
5. Are certain players more exposed than institutional players with dedicated compliance teams? Where's the weakest link right now?
Yes. About half of family offices have been hit by a cyberattack in the last 2 years, and 63% of them carry no cyber insurance at all. Firm size is only part of it, though, because exposure runs along the whole chain. A GP can have excellent internal controls and still lose capital because an LP's family office, a wealth manager, or the law firm coordinating a closing didn't. Attackers look for the weakest link and work from there. That's why separation of duties and verification have to reach everyone who touches the money, beyond your own four walls.
6. Fraud prevention often creates friction, extra verification steps, delays, additional approvals. How do you build protection into capital call and distribution workflows without slowing down transactions that need to move fast?
You stop treating verification as a step and start treating it as a layer that runs underneath the transaction. On 6lock, for example, identity and banking instructions are verified before any money moves. In the background, 6lock escalates signals that don’t fit that pattern to the GP or fund administrator: a new device, an unusual location, or a banking change in the 72 hours before a capital event. When an LP updates their own banking details directly on the platform, verified before it takes effect, that's actually less friction than the callback it replaces, not more. Speed and verification stop competing once verification isn't a manual task sitting in someone's inbox.
7. What's the hardest technical problem you've had to solve so far, detecting a cloned voice, verifying a video call is real, catching a compromised email thread, or something else entirely?
Honestly, the hardest problem sits underneath all three: running continuous verification at scale without creating false alarms that train people to ignore the system. The bigger question turned out to be whether we could verify intent without relying on whether the media itself is real, because media authenticity is a battle that keeps moving.
8. Does AI-driven fraud detection ever get ahead of AI-driven fraud generation, or is this a permanent game of catch-up?
If the goal is detecting fakes, it's a permanent arms race. Generation will keep improving, and detection will always be reacting to it. That's why we built 6lock around verifying identity and intent in a way that never depends on judging whether a call or an email is authentic. Verify the person and the instruction through an independent system of record, and it stops mattering how convincing the deepfake on the phone is, because the phone call was never the control.
9. If you're talking to someone at a fund who thinks "this won't happen to us," what's the one thing you'd want them to know?
"Our process has worked so far" is the most expensive sentence in private markets someone could say about money movement. A clean run on manual callbacks, emailed instructions, template uploads, and spreadsheets only tells you nobody has come for you yet. Voice cloning, compromised inboxes, and lookalike wires don't care that your last hundred capital events went fine. Companies have lost millions to emails sent from a lookalike domain, forcing them to suspend operations. The day it happens to you, you're explaining to LPs why you kept running fiduciary fund flows on an exposed system. That conversation is getting harder as LP operational due diligence deepens and verifiable controls over how capital moves become part of what fiduciary care means. You will answer for those controls in a diligence questionnaire or after a loss, and the questionnaire is cheaper.